Keycloak SCIM Provisioning
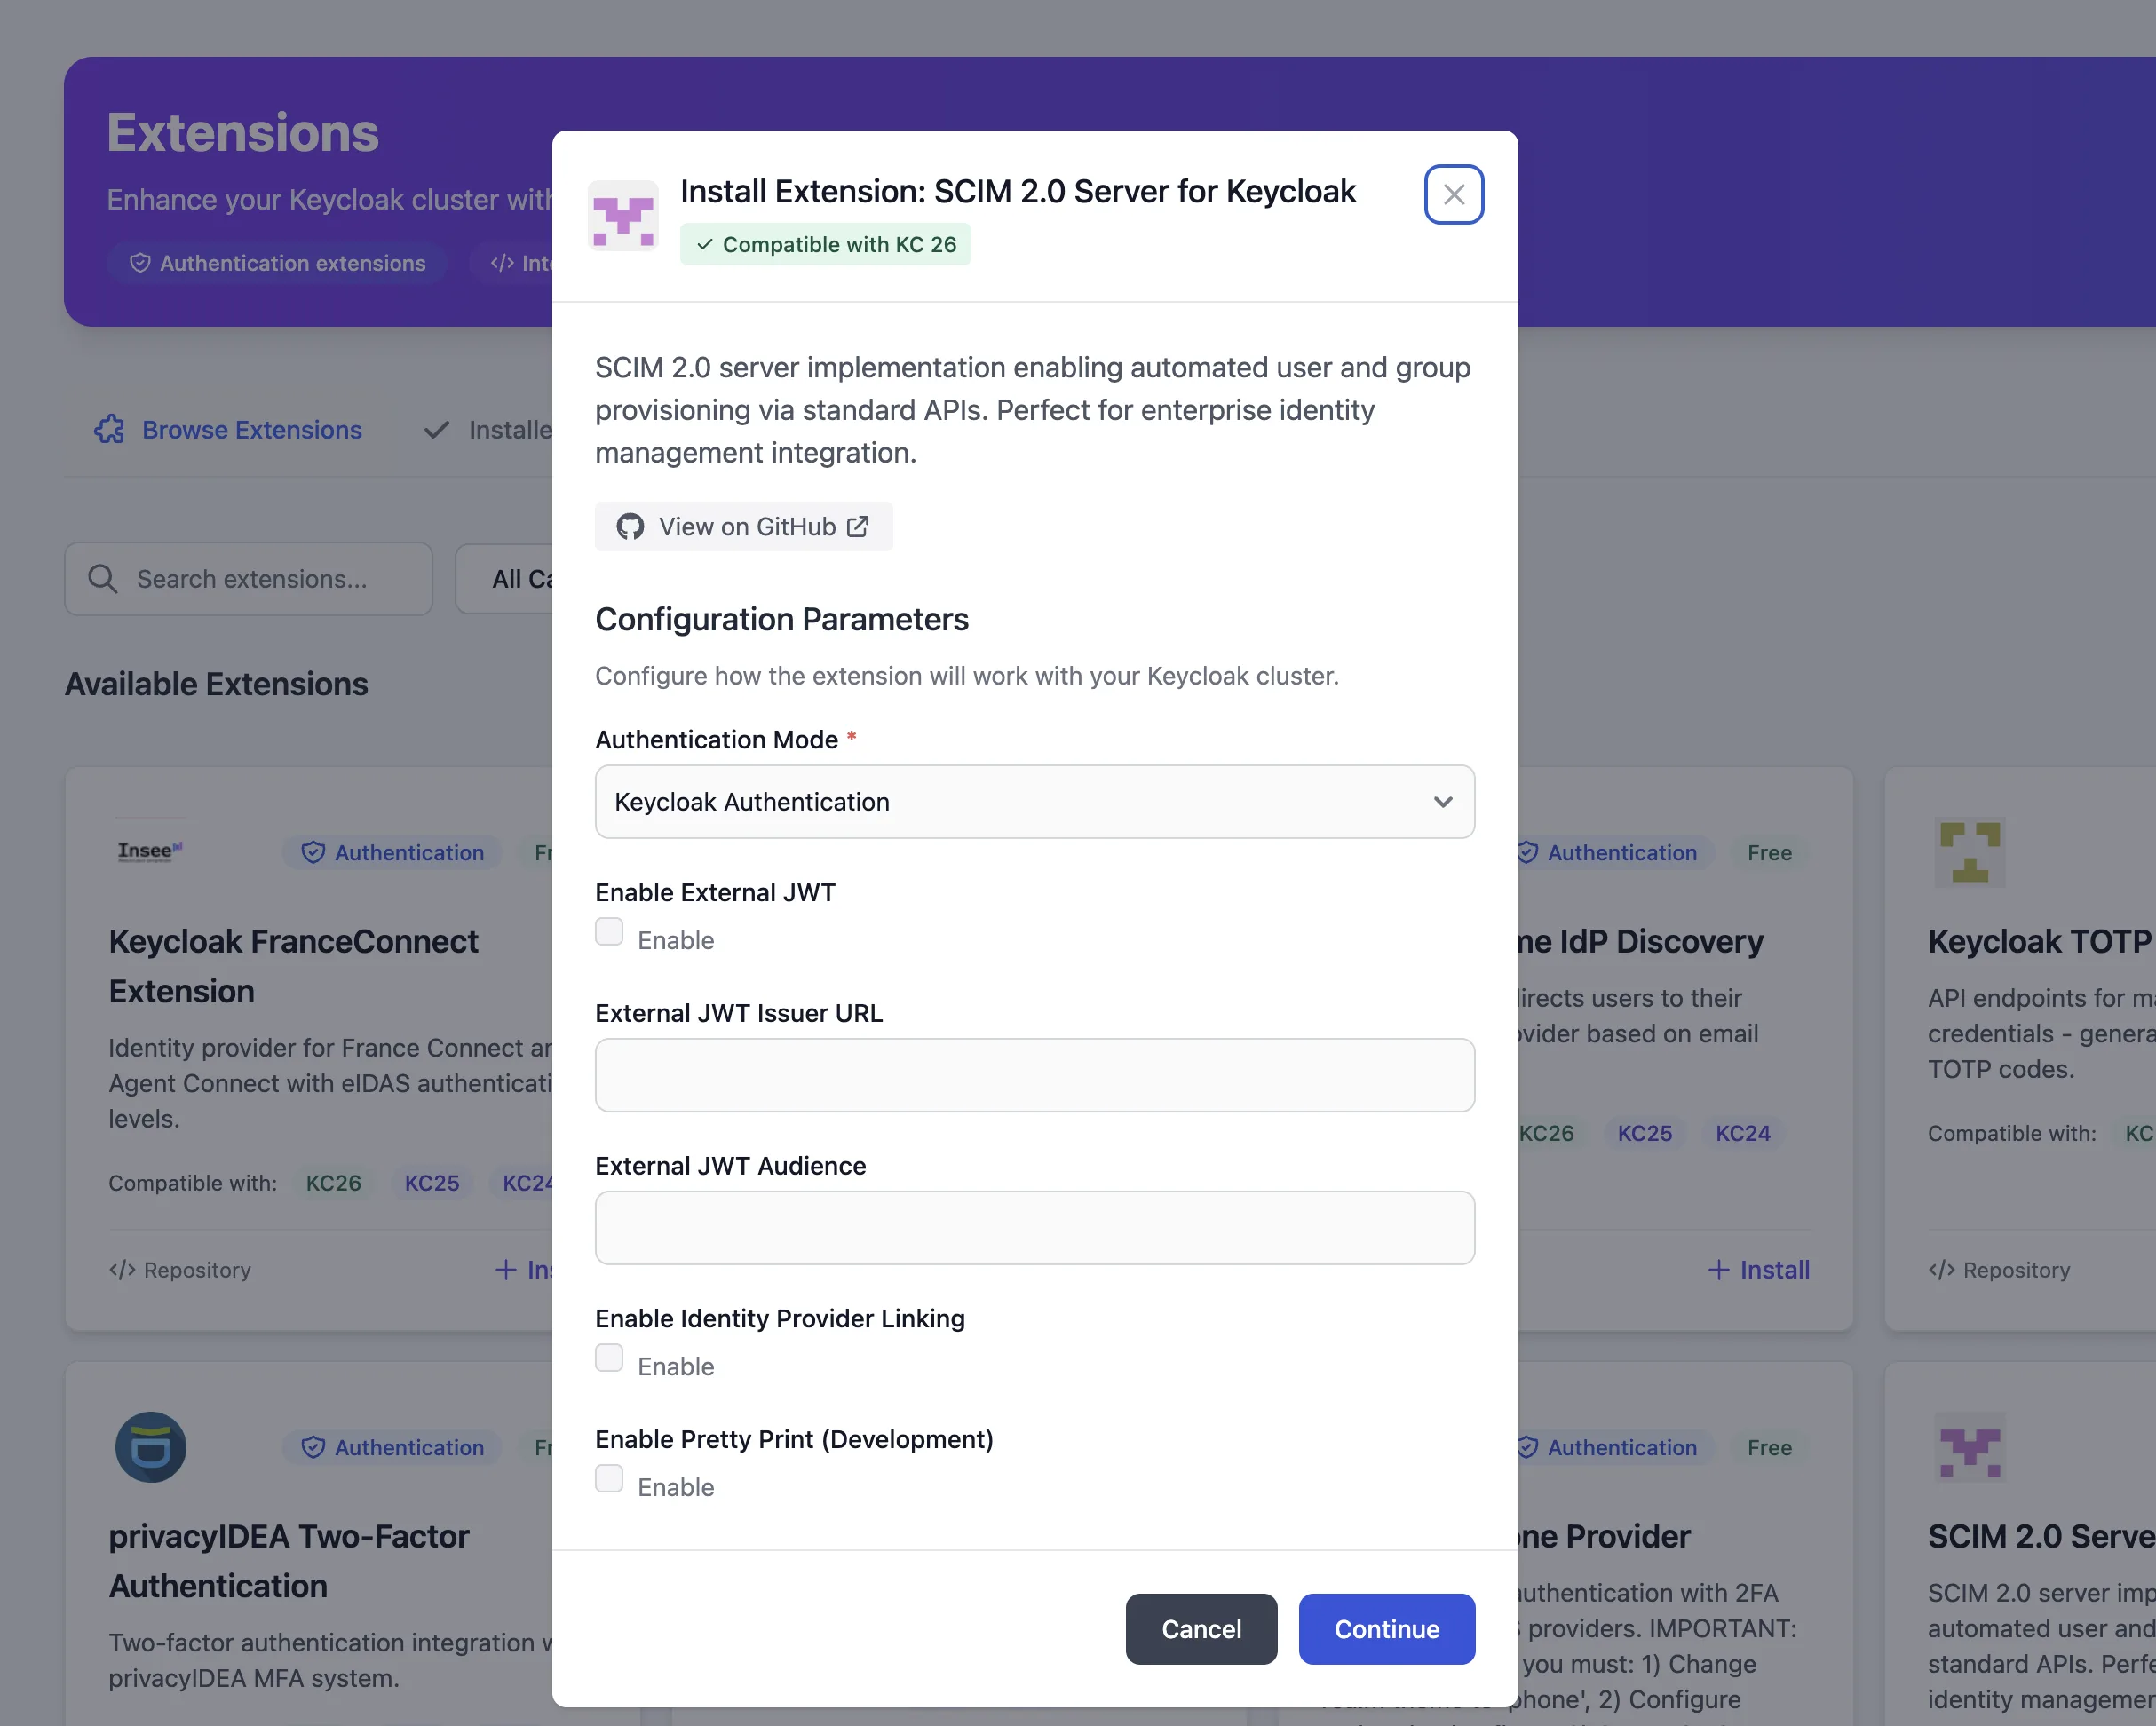
Automatic user lifecycle management for Keycloak via SCIM 2.0. Sync users from Okta, Azure AD, and other identity providers into Keycloak automatically.
21-day trial, no card required. · Runs on managed Keycloak.
What is SCIM Provisioning?
Automatic user provisioning and deprovisioning via SCIM 2.0.
SCIM Operations
Full SCIM 2.0 protocol support for user lifecycle.
Provisioning
Automatically create users when added to IdP.
Deprovisioning
Remove access instantly when users leave.
Group Sync
Keep groups and memberships in sync.
Enterprise Capabilities
Everything you need for secure, scalable authentication
Auto Provisioning
Create users automatically from IdP.
Deprovisioning
Remove access when users leave.
Group Sync
Sync groups and memberships.
SCIM 2.0
Standard protocol support.
Attribute Mapping
Map SCIM attributes to user fields.
Sync Logs
Track all provisioning events.
Compatible Identity Providers
SCIM-enabled providers for automatic sync
Enterprise IdPs
Full SCIM support Okta
 Azure AD
 OneLogin
HR Systems
SCIM connectors Workday
 BambooHR
 Rippling
{
  "schemas": ["urn:ietf:params:scim:schemas:core:2.0:User"],
  "userName": "john.doe@example.com",
  "name": {
    "givenName": "John",
    "familyName": "Doe"
  },
  "emails": [{
    "value": "john.doe@example.com",
    "primary": true
  }],
  "active": true
}
Go Live in 3 Steps
From zero to production in minutes, not months
Create Your Instance
Sign up and deploy your Keycloak instance. One click, fully managed.
2 minutesCustomize Your Branding
Add your logo, colors, and styling to make login pages match your brand.
5 minutesIntegrate Your App
Use existing Keycloak SDKs or standard OIDC/SAML libraries for any framework.
15 minutesNo credit card required. 21-day free trial with full access.
Related Features
Complement your setup with these capabilities
Ready to Get Started?
Start your free trial today. Full access to all features for 21 days.