Articles by Guilliano Molaire
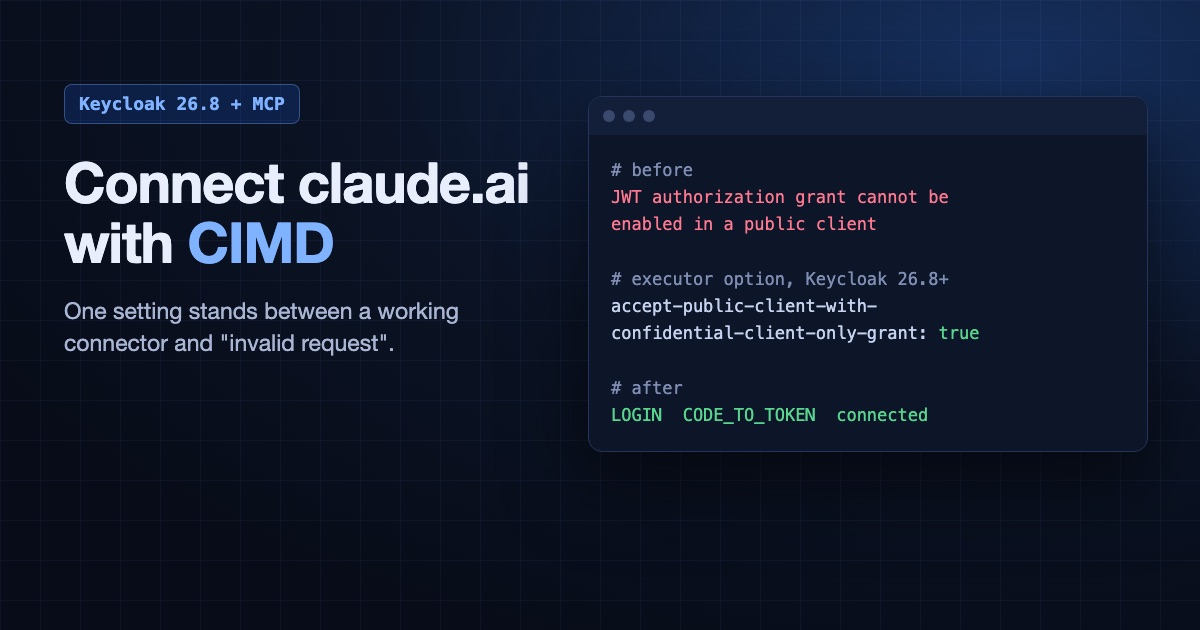
Connect claude.ai to Keycloak with CIMD: Fix the JWT Grant Error
claude.ai fails on Keycloak CIMD with a JWT grant error in public clients. Here is the tested fix: Keycloak 26.8,…
7 min read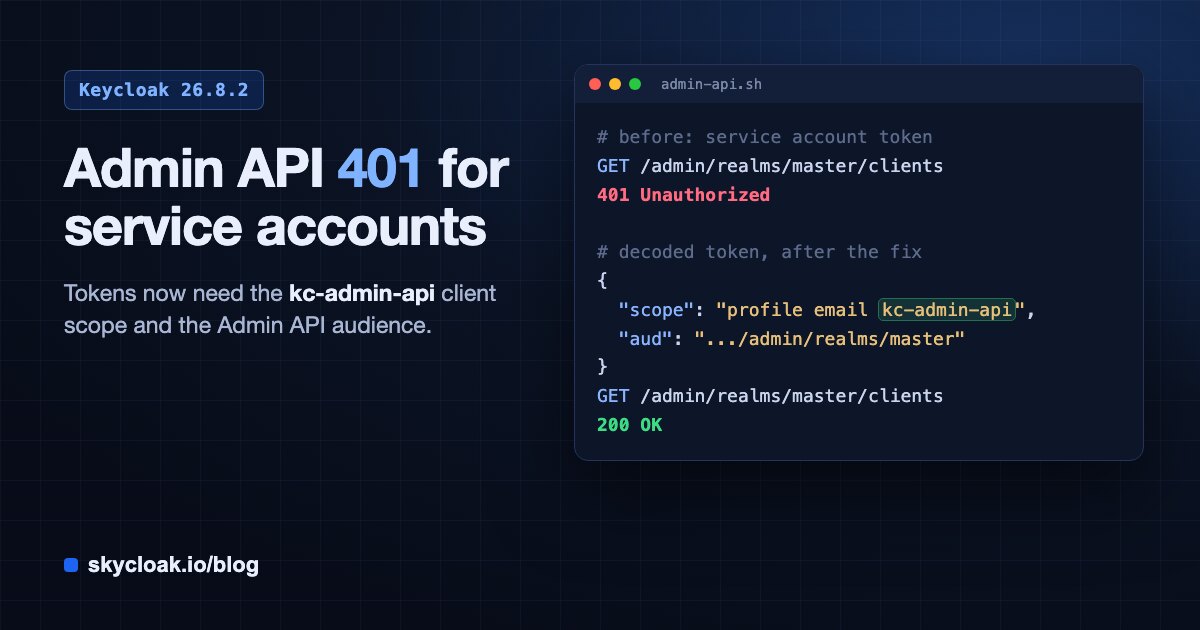
Keycloak 26.8.2 Admin API Returns 401 for Service Accounts: The kc-admin-api Scope Fix
After upgrading to Keycloak 26.8.2, service account tokens get 401 from the Admin REST API. Why the new audience check…
7 min readKeycloak as an Identity Provider for Cloudflare Access
Use Keycloak as an OIDC identity provider for Cloudflare Access (Zero Trust): configure the integration, pass groups for policies, and…
10 min readSecuring Hasura GraphQL with Keycloak JWT Claims
Secure Hasura GraphQL with Keycloak: configure JWT mode, add the x-hasura-* custom claims via a protocol mapper, and map Keycloak…
10 min read
Ivanti Connect Secure CVE-2026-111357 Exploited: What to Do
CISA added Ivanti Connect Secure CVE-2026-111357 and CVE-2026-118527 to the KEV catalog on 30 October 2026. Upgrade, reset, rotate and…
13 min readBeyondTrust CVE-2026-102764: Patch, Audit, Rotate
CVE-2026-102764 is an exploited auth bypass in BeyondTrust Remote Support 26.2.3 and earlier. Patch BT26-05, then what to audit and…
15 min readRegulatory Compliance in IAM: What Auditors Check at Login
Regulatory compliance in IAM means proving who could log in, with what rights, and when. What SOC 2, HIPAA, PCI…
18 min readKeycloak Client Authentication Without Secrets: Signed JWT (private_key_jwt)
Replace Keycloak client secrets with Signed JWT (private_key_jwt): the client signs a short assertion with its own key. Setup, code,…
9 min readAuthentication vs Authorization: Why Valid Logins Get 403
Authentication proves who is calling, authorization decides what they may do. See a Keycloak token pass every check and still…
18 min readPHP2Shell (CVE-2026-109618): Patch PHP, Rotate Login Secrets
PHP2Shell (CVE-2026-109618, CVE-2026-109619): unauthenticated RCE in PHP. Fixed in 8.2.35, 8.3.36, 8.4.27, 8.5.12. Patch order, mitigations, what to rotate.
22 min read