security
Articles about security from the Skycloak team.
Keycloak 26.8.1 SAML Logout Fix: One Client Could End Another's Sessions
Keycloak 26.8.1 changes how SAML single logout treats a SessionIndex owned by another client. What the code did before, what…
 6 min read
What Is Password Spraying? vs Credential Stuffing, and How to Stop It
Password spraying tries a few common passwords on many accounts, so no lockout fires. How it differs from credential stuffing,…
6 min readWhat Is Session Fixation? How It Differs From Session Hijacking
Session fixation plants a known session ID before the victim logs in. How it differs from session hijacking, where it…
6 min readCVE-2026-107121: Keycloak SMTP StartTLS Plaintext Downgrade
Keycloak 26.8.1 fixes CVE-2026-107121: realm SMTP with StartTLS on could still send credentials in plaintext. What changed, who is affected,…
8 min readKeycloak CVE-2026-103884: X.509 CRL Path Traversal When CRL Checking Is On
CVE-2026-103884 lets a crafted client certificate steer Keycloak's X.509 CRL loader outside its conf directory. Who is exposed, the real…
12 min readWhat Is Account Takeover (ATO)? How SaaS Teams Detect and Prevent It
Account takeover (ATO) means an attacker controls a real user's account. How it differs from a breach, the seven entry…
14 min readSession Hijacking: Why MFA Doesn't Save a Stolen Session
Session hijacking uses a stolen cookie or token, so MFA never fires. How infostealers do it, what limits the damage,…
8 min readWhat Is Credential Stuffing? Vs Brute Force, and How to Stop It
Credential stuffing replays leaked username and password pairs against your login. How it differs from brute force, what to watch…
7 min readBetter Auth 1.7.7: OAuth State vs Magic-Link Tokens
Better Auth 1.7.7 stops OAuth state values being redeemed as magic-link tokens. What went wrong, how to upgrade, and how…
11 min read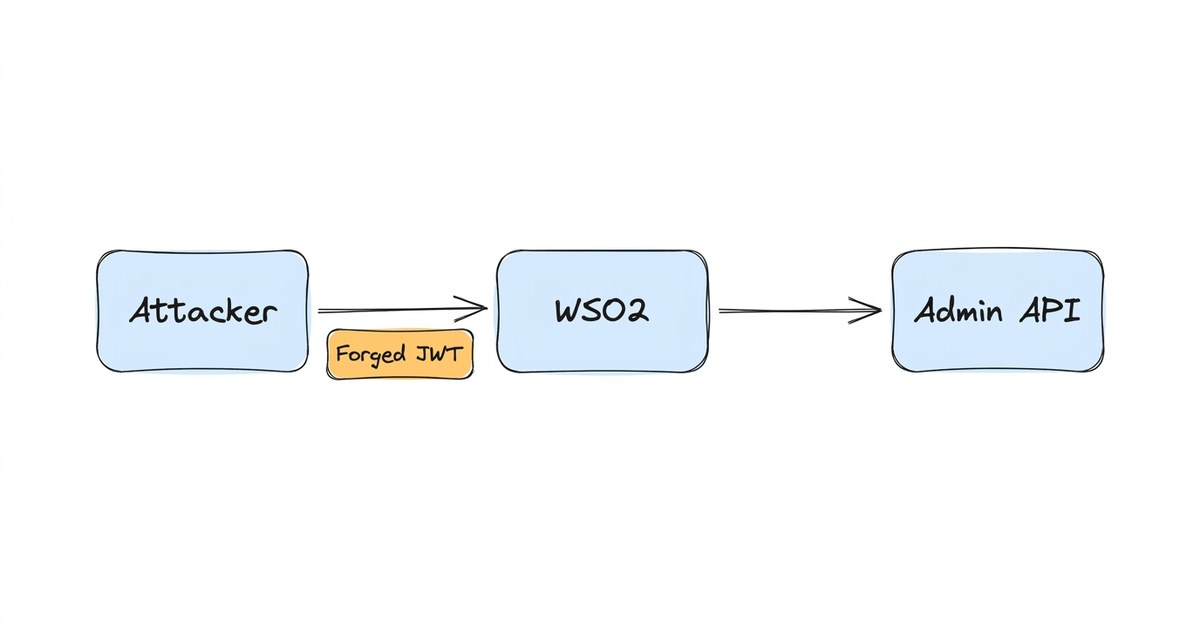
CVE-2026-5430: WSO2 JWT Bypass, PoC Status and Detection
CVE-2026-5430 lets forged JWTs past WSO2 API Manager auth. See affected versions, public PoC status, how to detect exploitation and…
16 min readStay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.