cve
Articles tagged with cve.
Ivanti Connect Secure CVE-2026-111357 Exploited: What to Do
CISA added Ivanti Connect Secure CVE-2026-111357 and CVE-2026-118527 to the KEV catalog on 30 October 2026. Upgrade, reset, rotate and…
 13 min read
Aruba AOS Auth Bypass: Patch, Then Rotate Secrets
HPE fixed eight CVSS 10.0 flaws in Aruba AOS-8 and AOS-10, auth bypasses among them. The CVEs, fixed versions, and…
 15 min read
BeyondTrust CVE-2026-102764: Patch, Audit, Rotate
CVE-2026-102764 is an exploited auth bypass in BeyondTrust Remote Support 26.2.3 and earlier. Patch BT26-05, then what to audit and…
15 min readPHP2Shell (CVE-2026-109618): Patch PHP, Rotate Login Secrets
PHP2Shell (CVE-2026-109618, CVE-2026-109619): unauthenticated RCE in PHP. Fixed in 8.2.35, 8.3.36, 8.4.27, 8.5.12. Patch order, mitigations, what to rotate.
22 min readApache CXF CVE-2026-50627: JWT Audience Checks for Keycloak APIs
CVE-2026-50627 let Apache CXF skip the JWT audience claim check. Here is what every resource server must validate on Keycloak…
12 min readOpenAM PKCE Bypass and JWKS SSRF (2026): Lessons for Keycloak OIDC Clients
OpenAM before 16.1.3 skipped PKCE on hybrid flows (CVE-2026-105119) and fetched unvalidated jwks_uri values (CVE-2026-105122). Here is the Keycloak checklist.
11 min readCVE-2026-107121: Keycloak SMTP StartTLS Plaintext Downgrade
Keycloak 26.8.1 fixes CVE-2026-107121: realm SMTP with StartTLS on could still send credentials in plaintext. What changed, who is affected,…
8 min readKeycloak CVE-2026-103884: X.509 CRL Path Traversal When CRL Checking Is On
CVE-2026-103884 lets a crafted client certificate steer Keycloak's X.509 CRL loader outside its conf directory. Who is exposed, the real…
12 min read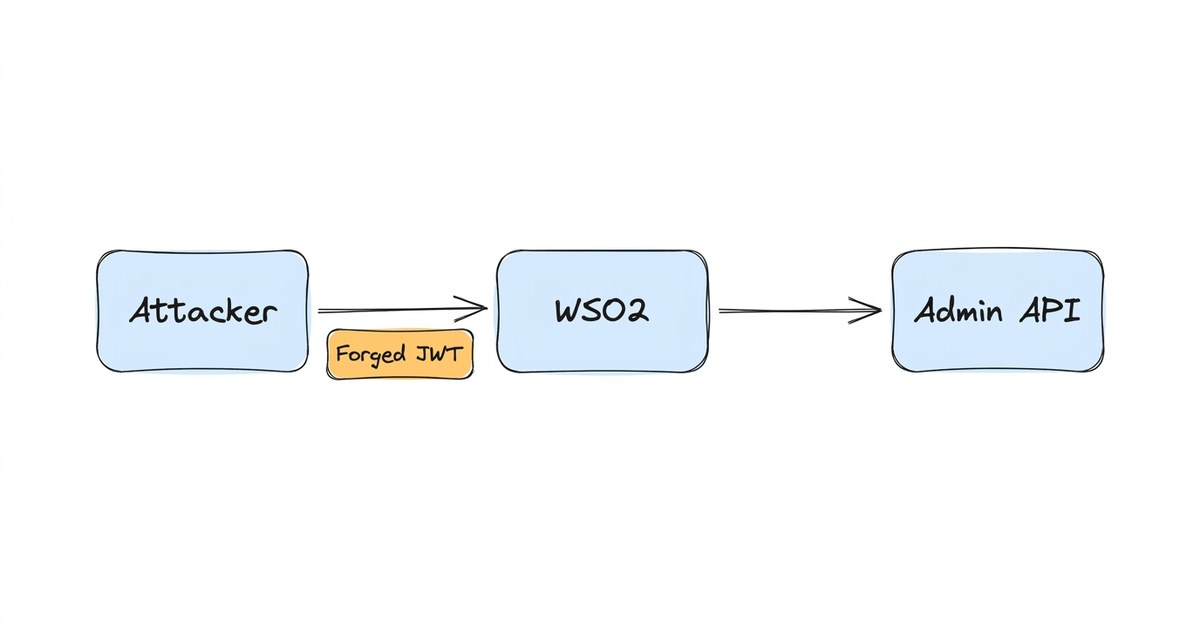
CVE-2026-5430: WSO2 JWT Bypass, PoC Status and Detection
CVE-2026-5430 lets forged JWTs past WSO2 API Manager auth. See affected versions, public PoC status, how to detect exploitation and…
16 min readCVE-2026-100606: Flowise SSO Invite Takeover and IdP Checks
CVE-2026-100606 lets anyone who signs in with an invitee's email take over a pending Flowise Enterprise invite. How it works…
9 min readStay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.