keycloak
Articles tagged with keycloak.
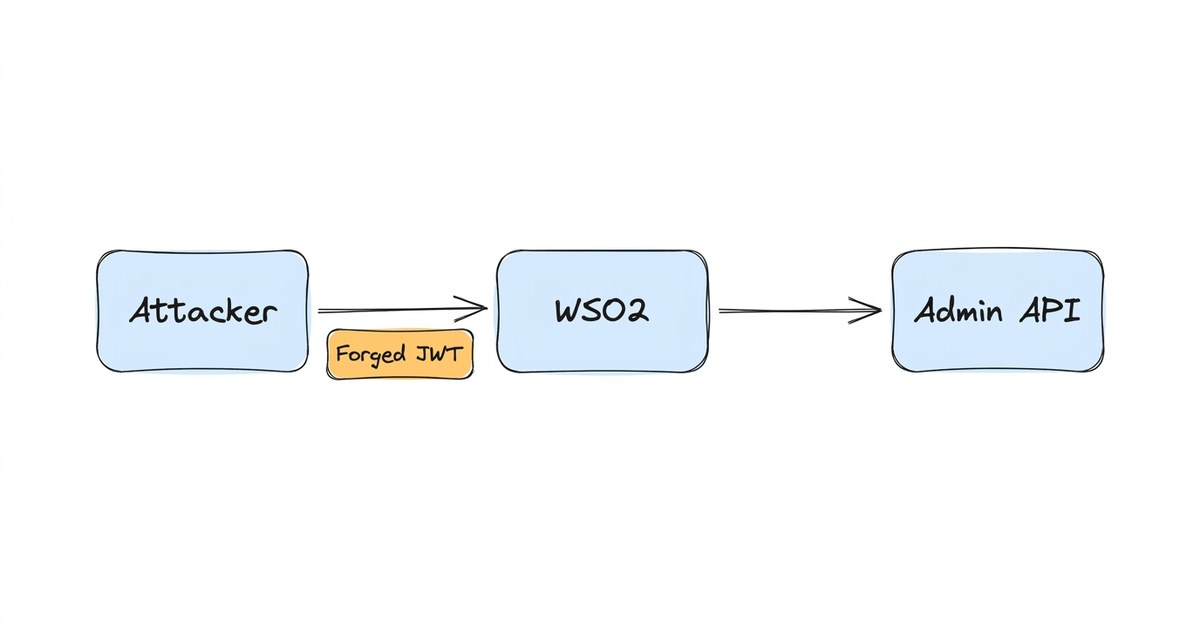
CVE-2026-5430: WSO2 JWT Bypass, PoC Status and Detection
CVE-2026-5430 lets forged JWTs past WSO2 API Manager auth. See affected versions, public PoC status, how to detect exploitation and…
 16 min read
Microsoft Entra Agent ID vs Keycloak for AI Agent Identity
Microsoft Entra Agent ID gives AI agents directory identities. Here is how blueprints, FIC and agent OBO map to Keycloak…
13 min readOkta Agent Gateway vs Keycloak for MCP Authorization
Okta Agent Gateway puts policy inline between AI agents and MCP tools. Here is what it adds, and why MCP…
12 min readMCP Python SDK OAuth Flaw: Pin the Issuer on Keycloak
MCP OAuth flaw GHSA-qx49-fqc8-xw99: a malicious server could steal client secrets and PKCE verifiers from the MCP Python SDK. Upgrade,…
12 min readCVE-2026-100606: Flowise SSO Invite Takeover and IdP Checks
CVE-2026-100606 lets anyone who signs in with an invitee's email take over a pending Flowise Enterprise invite. How it works…
9 min readJADEPUFFER and Storm-3168: Retire Static Keycloak Secrets
Storm-3168 (JADEPUFFER) wiped Azure resources with compromised service principals. How the same client secret risk looks on Keycloak, and how…
12 min readCVE-2026-96448: Keycloak FGAP Composite Privilege Escalation
CVE-2026-96448 is a Keycloak privilege escalation: an FGAP v2 delegated admin assigns a composite role that hides realm-admin. How it…
11 min readKeycloak 26.7.4 Security Fixes: A Self-Hosted Patch Checklist
Keycloak 26.7.4 fixes six CVEs, from a SAML memory leak to impersonation of realm admins. Which reach 26.6 and 26.4,…
10 min readCVE-2026-19607: Keycloak Username Takeover and Account Lockout
CVE-2026-19607: a brokered login whose email matches a Keycloak username shadows that user and locks them out. Fixed in 26.7.4.…
11 min readCVE-2026-97176: Keycloak Step-Up Authentication Bypass
CVE-2026-97176 can let Keycloak issue a token at a lower assurance level than a client's essential acr demands, skipping step-up.…
9 min readStay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.