api-security
Articles tagged with api-security.
Apache CXF CVE-2026-50627: JWT Audience Checks for Keycloak APIs
CVE-2026-50627 let Apache CXF skip the JWT audience claim check. Here is what every resource server must validate on Keycloak…
 12 min read
CVE-2026-5430: WSO2 JWT Bypass and Your Keycloak APIs
CVE-2026-5430 let forged JWTs past WSO2 API Manager authentication. Here is how you pin algorithms and fail closed on APIs…
12 min readToken Introspection vs Local JWT Validation in Keycloak
Keycloak token introspection vs local JWT validation: how each works, the latency and revocation trade-offs, and which to use for…
10 min readAPI Authentication Best Practices in 2026
Comprehensive guide to API authentication in 2026 covering OAuth 2.0 with PKCE, mTLS, DPoP, JWT validation, token introspection, and choosing…
7 min readAPI Keys vs OAuth: When to Use Each with Keycloak
Decision guide comparing API keys and OAuth tokens for API security. Learn when to use each approach, hybrid patterns, and…
9 min readKeycloak + Go: Build Secure APIs with gocloak
Complete guide to securing Go APIs with Keycloak using gocloak. Covers JWT validation, RBAC middleware, token introspection, and gin router…
9 min readFastAPI Authentication with Keycloak: Securing Python APIs
Step-by-step guide to securing FastAPI APIs with Keycloak using JWT validation, role-based access control, and token introspection in Python applications.
10 min read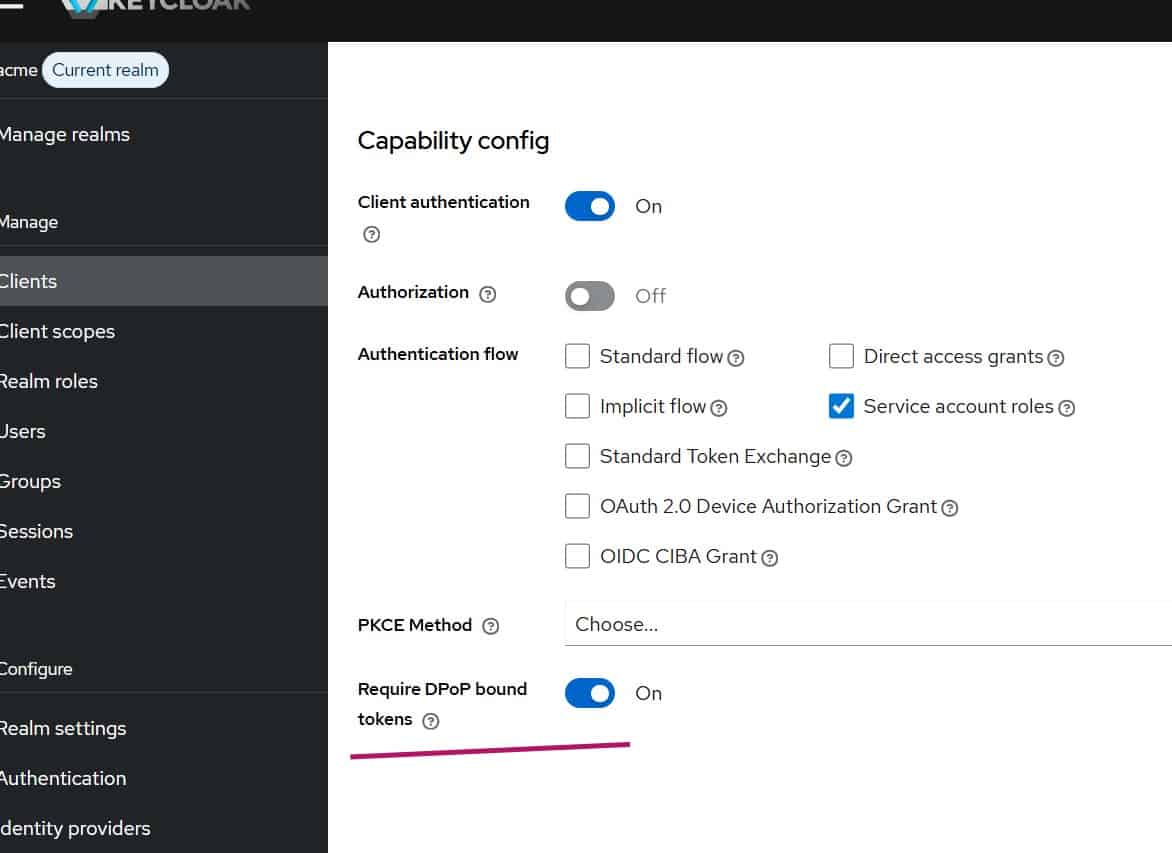
DPoP with Keycloak Admin API Using Node.js
Implement DPoP proof-of-possession tokens with Keycloak Admin API using Node.js to prevent token replay attacks and secure API access.
 5 min read
Keycloak Token Validation for APIs
Learn how to validate Keycloak tokens for API security using local JWT verification, token introspection, and framework integrations.
10 min readStay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.