jwt
Articles tagged with jwt.
ML-DSA Signature Size and the 4 KB Cookie Limit (Keycloak Prep)
ML-DSA signatures run 2,420 to 4,627 bytes against RS256's 256 bytes. The token size math, the 4 KB cookie wall…
 10 min read
JWT Token Lifecycle: Expiration, Refresh, and Revocation
JWT lifecycle guide: expiration, refresh token rotation per RFC 9700, Keycloak revocation, and Spring Boot resource server validation with zero…
11 min read
Session Management: Cookies vs Tokens vs Server-Side
Cookies vs tokens vs server-side sessions for distributed systems: security trade-offs, 2026 cookie changes, and how Keycloak persists sessions by…
11 min read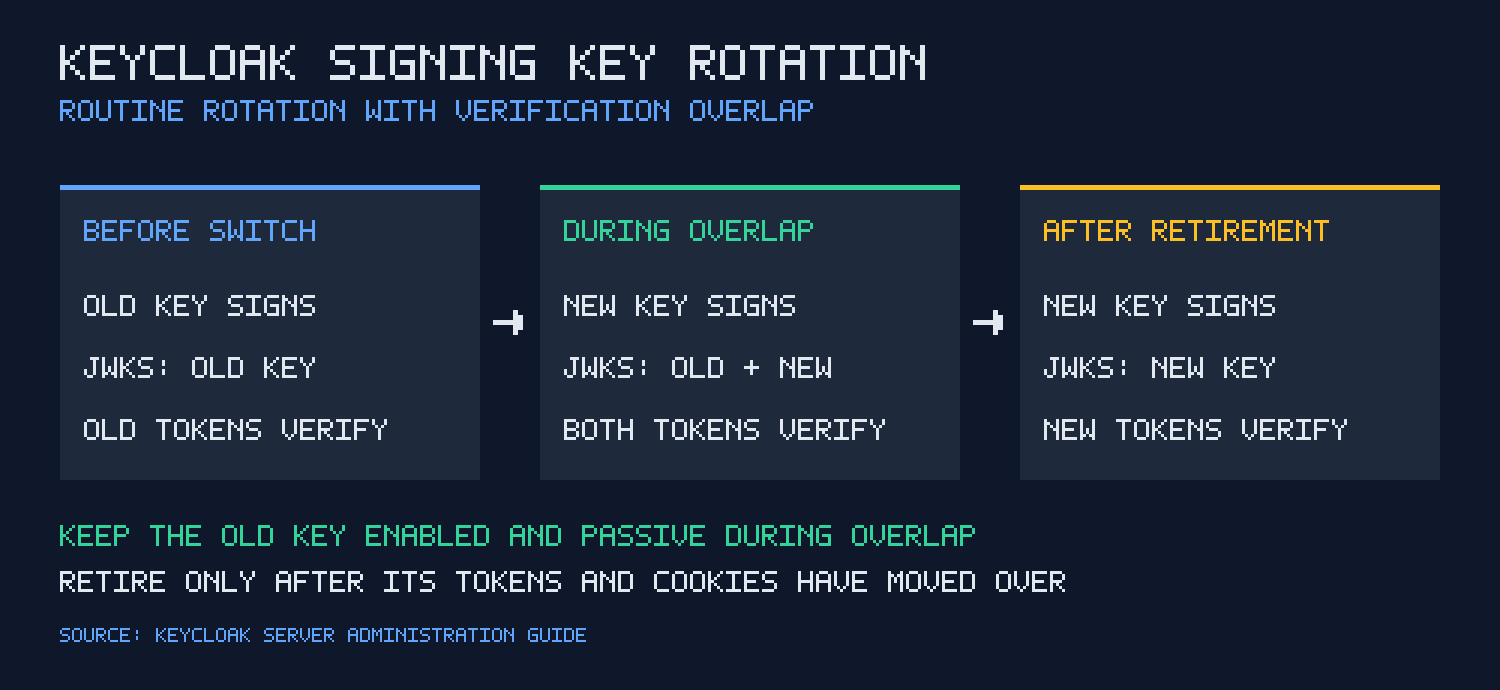
JWKS Explained: JSON Web Key Sets and Keycloak Key Rotation
Learn what JWKS means, how to verify JWT signatures safely, and how to rotate Keycloak signing keys with overlap while…
13 min read
How to Verify a Keycloak Access Token on the Backend
Verify Keycloak access tokens on your backend: local JWT signature checks with JWKS, token introspection, claim validation, and Java, Node,…
11 min readKeycloak 'Token Not Active' Clock Skew: How to Fix
Fix Keycloak 'token is not active' and 'JWT issued in the future' errors caused by clock skew: sync server time…
7 min readToken Introspection vs Local JWT Validation in Keycloak
Keycloak token introspection vs local JWT validation: how each works, the latency and revocation trade-offs, and which to use for…
10 min read
Keycloak Authentication in ASP.NET Core (.NET 8)
Secure an ASP.NET Core (.NET 8) API and web app with Keycloak: OpenID Connect login, JWT bearer validation, role-based authorization,…
11 min readJWT Best Practices: Security, Storage, and Rotation
A comprehensive guide to JWT security best practices covering token storage, key rotation, claim validation, refresh token rotation, and Keycloak…
11 min read
Keycloak JWT Authorization Grant with a Node.js Token Issuer
Set up the Keycloak JWT authorization grant (RFC 7523) with a Node.js app that signs assertions: identity provider, client, user…
 14 min read
Stay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.