jwt
Articles tagged with jwt.
Securing Hasura GraphQL with Keycloak JWT Claims
Secure Hasura GraphQL with Keycloak: configure JWT mode, add the x-hasura-* custom claims via a protocol mapper, and map Keycloak…
 10 min read
JWT Vulnerabilities: Algorithm Confusion, None Alg and Safe Validation
Most JWT vulnerabilities come from trusting the header. See each attack, from alg none to algorithm confusion and kid injection,…
 19 min read
What Is an RSA Key and How Identity Providers Sign Tokens
An RSA key is a public and private key pair. Identity providers sign JWTs with RS256, publish the public key…
15 min readAuthentication vs Authorization: Why Valid Logins Get 403
Authentication proves who is calling, authorization decides what they may do. See a Keycloak token pass every check and still…
18 min readApache CXF CVE-2026-50627: JWT Audience Checks for Keycloak APIs
CVE-2026-50627 let Apache CXF skip the JWT audience claim check. Here is what every resource server must validate on Keycloak…
12 min readJWT sub Claim Explained: Unique Only Per Issuer
The JWT sub claim identifies a user only within one issuer. Why your key must be iss plus sub, why…
8 min readWhat Is a Bearer Token? How Bearer Authentication Works
A bearer token grants access to whoever holds it. How to send it in the Authorization header, opaque vs JWT…
16 min readWhat Is a JWT Token? Structure, Claims and Signatures
A JWT token is a signed Base64URL string with a header, payload and signature. What each part holds, which claims…
12 min readID Token vs Access Token: Differences and How to Validate
An ID token tells your app who signed in; an access token tells an API what the caller may do.…
7 min read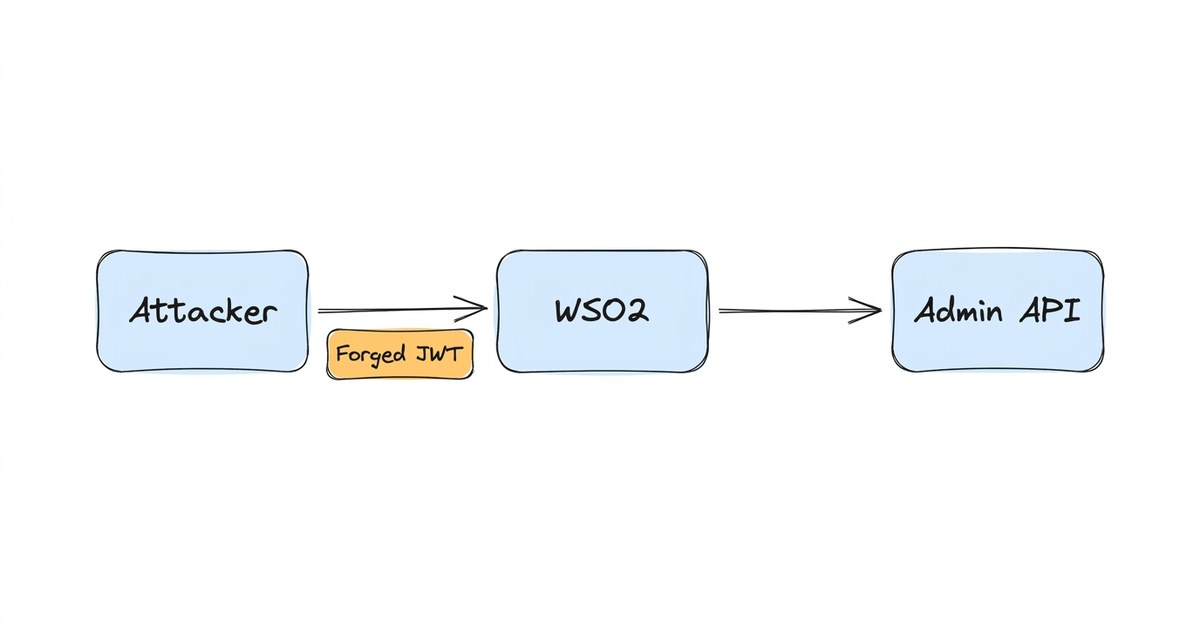
CVE-2026-5430: WSO2 JWT Bypass, PoC Status and Detection
CVE-2026-5430 lets forged JWTs past WSO2 API Manager auth. See affected versions, public PoC status, how to detect exploitation and…
16 min readStay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.