security
Articles tagged with security.
Geo-Blocking Your Keycloak Cluster Using Skycloak
Learn how to restrict access to your Keycloak cluster by country using Skycloak's built-in geo-blocking, reducing attack surface and meeting…
 8 min read
Forward Keycloak Events to SIEM via Skycloak HTTP Webhook
Learn how to forward Keycloak authentication events, server logs, and security telemetry to your SIEM platform using Skycloak HTTP webhook…
 4 min read
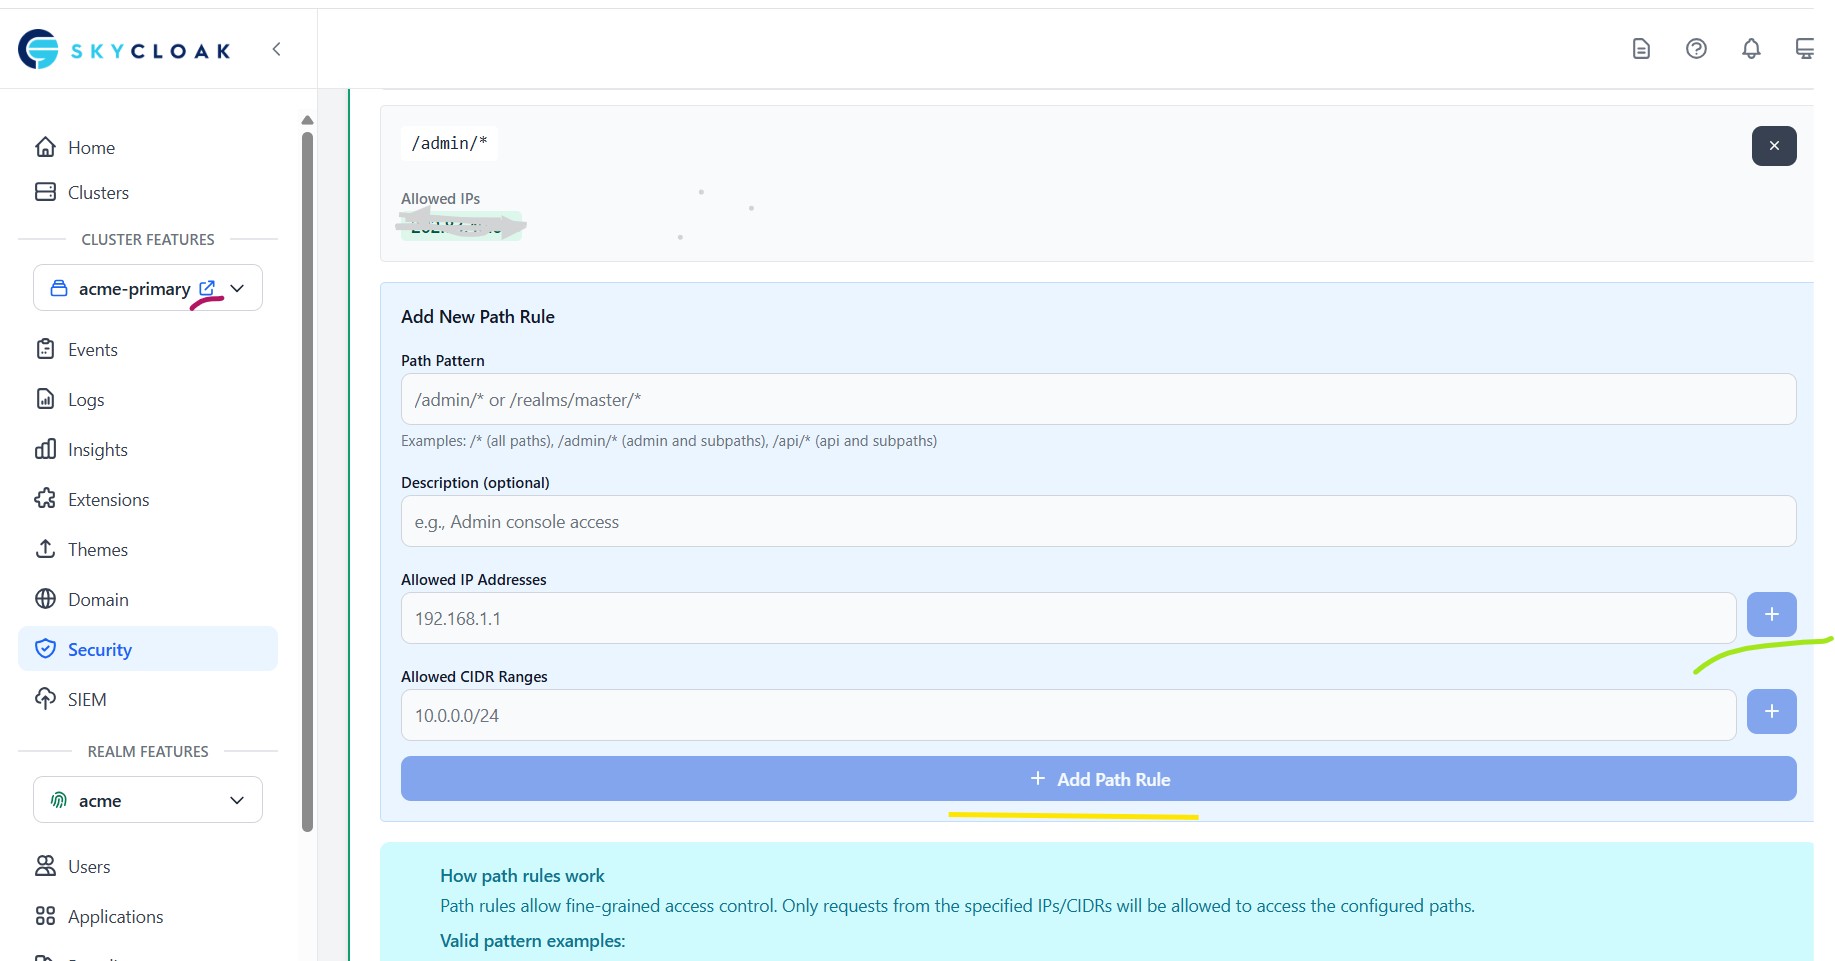
Path-Based IP Restriction for Keycloak Admin Console
Restrict Keycloak admin console access using IP and CIDR-based whitelisting on Skycloak to secure the /admin/* path from unauthorized access.
3 min read
Keycloak ABAC Configuration: Step-by-Step Guide
Learn how to configure Attribute-Based Access Control (ABAC) in Keycloak with this step-by-step guide covering policies, resources, and permissions.
10 min read
Keycloak SAML Security: Vulnerabilities and Hardening
Explore Keycloak SAML security vulnerabilities including CVE-2024-8698, XML wrapping attacks, and assertion replay, with hardening steps.
11 min read
Session Management in Keycloak: From Refresh to Idle Timeouts
How Keycloak session management works: access, refresh and ID tokens, the SSO idle and session-max timeouts, token lifespans, and security…
7 min read
Context-Aware Access Control in Keycloak: How It Works
What context-aware access control is, how it differs from RBAC and ABAC, and how to build time, network and device…
16 min read
Reducing Insider Risk with IAM Security Measures
Learn how to reduce insider risk with IAM security measures in Keycloak, including RBAC, MFA, audit logging, and zero trust…
9 min read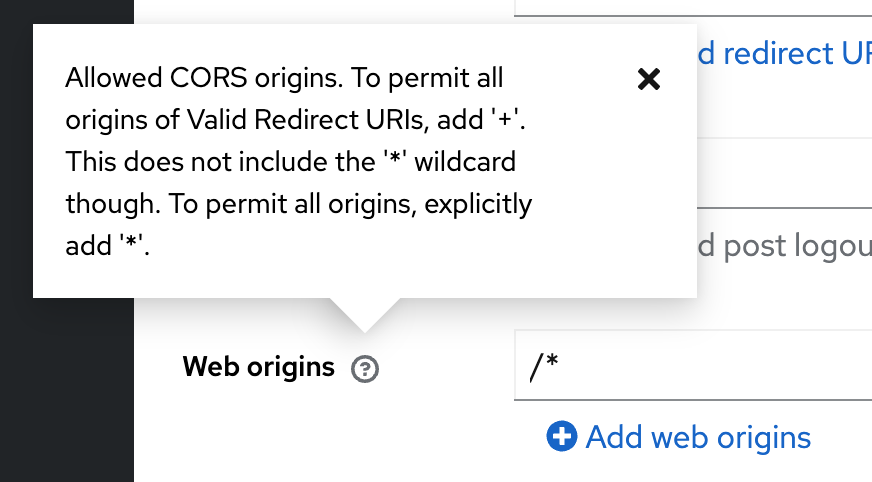
Configuring CORS with Your Keycloak OIDC Client
Learn how to configure CORS for Keycloak OIDC clients, fix common cross-origin errors, and secure browser-based apps with proper Web…
9 min read
Implementing RBAC in Keycloak: Roles, Scopes, and Policies
Learn how to implement RBAC in Keycloak with realm roles, client roles, policies, and JWT token mapping for secure authorization.
10 min readStay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.