Insights on Identity, Security & Keycloak
Tutorials, deep dives, and best practices from the Skycloak team.
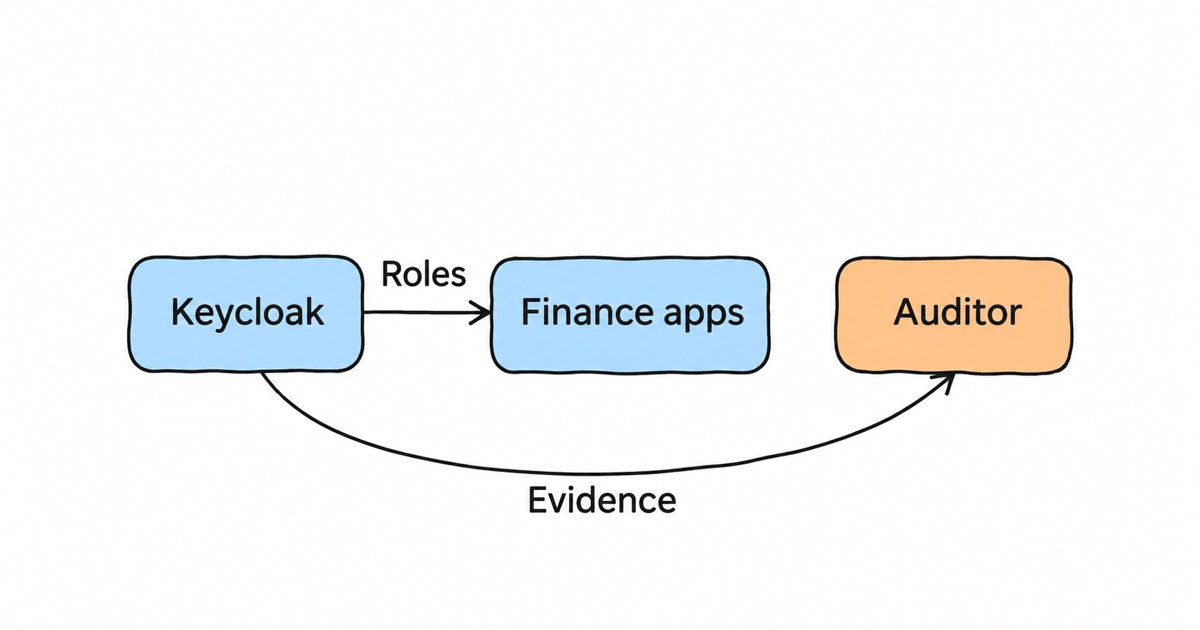
Sarbanes-Oxley and Access Control: What SOX Asks of IAM
The Sarbanes-Oxley Act makes public companies prove their financial reporting is accurate. See what Section 404 asks of logins, roles,…
 15 min read
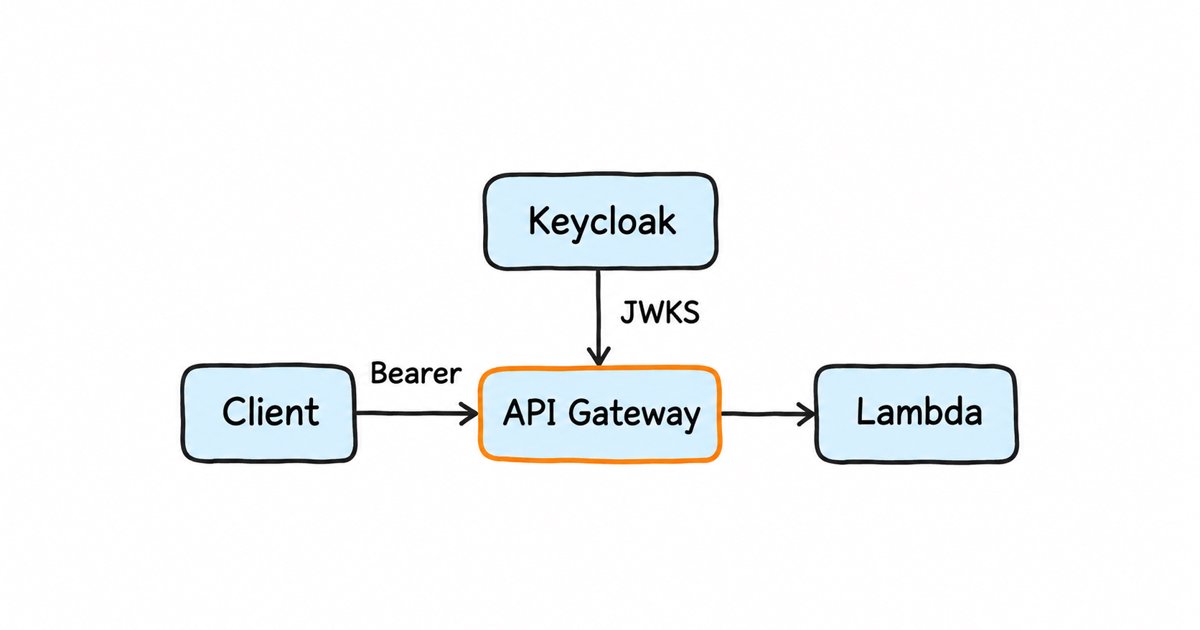
Secure AWS API Gateway with Keycloak Using a JWT Authorizer
Secure AWS API Gateway with Keycloak using an HTTP API JWT authorizer: set the issuer, add an audience mapper, map…
 10 min read
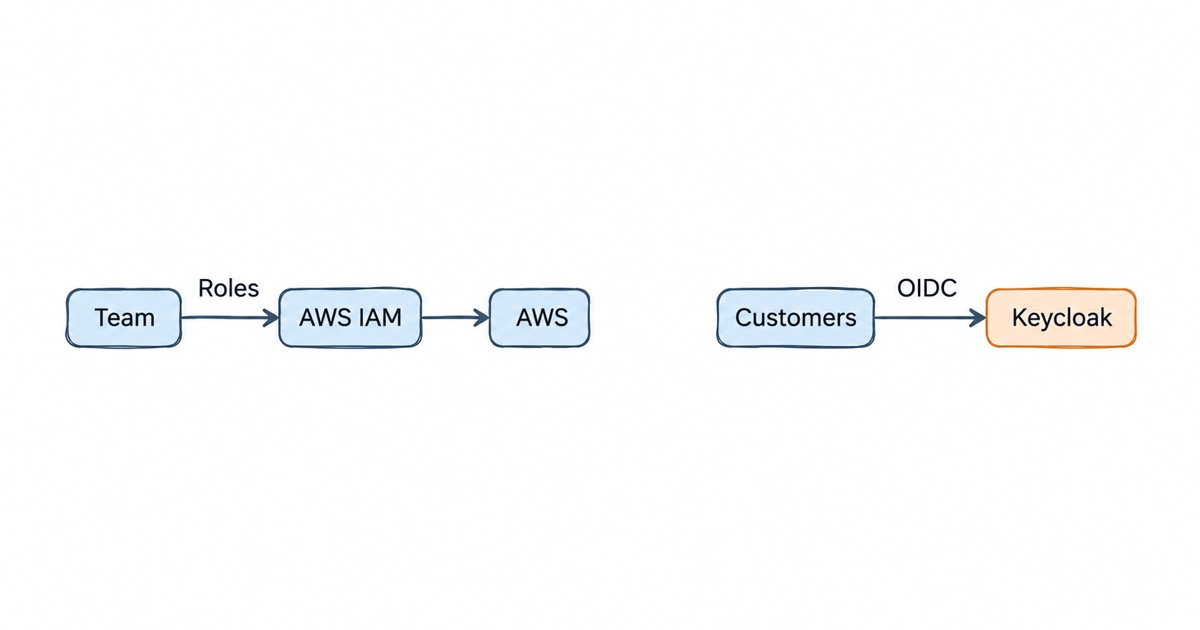
AWS IAM Explained: What It Covers and What It Does Not
AWS IAM controls who and what can access your AWS account. Learn users, groups, roles and policies, what IAM costs,…
10 min read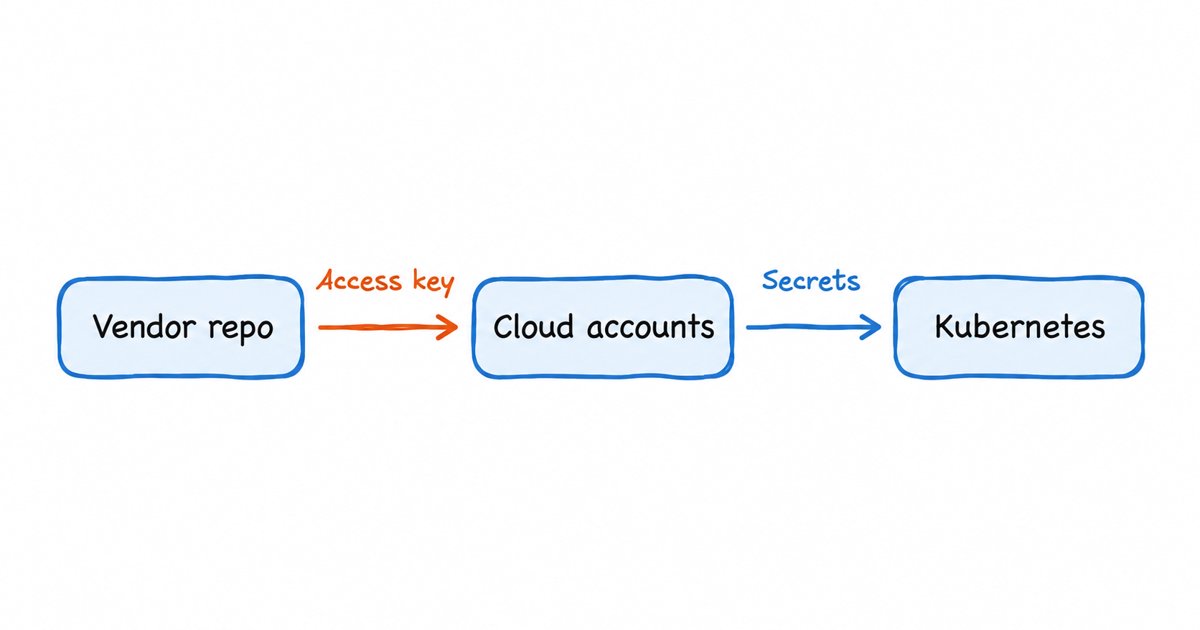
Barracuda cloud breach: what a stolen access key can open
Barracuda's cloud breach began with a vendor access key that was never retired. What it opened, how ARTEX sped it…
13 min read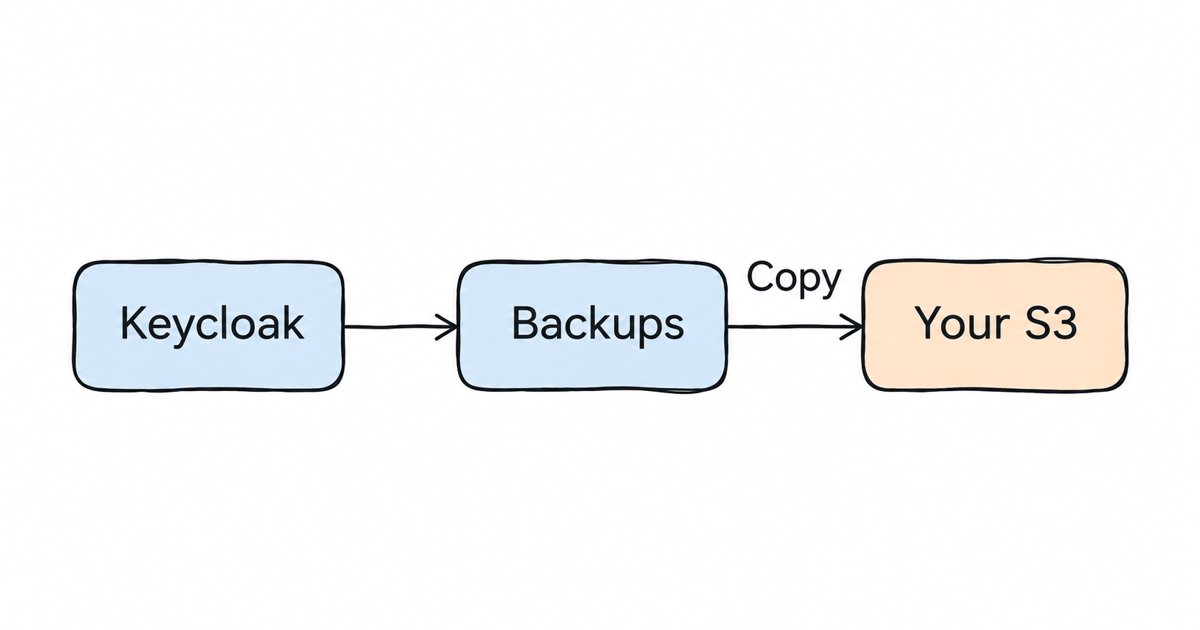
How to Keep Off-Site Keycloak Backups in Your Own S3 Bucket
Skycloak can copy each managed Keycloak backup to an AWS S3 bucket you own. Create the bucket, give Skycloak a…
 10 min read
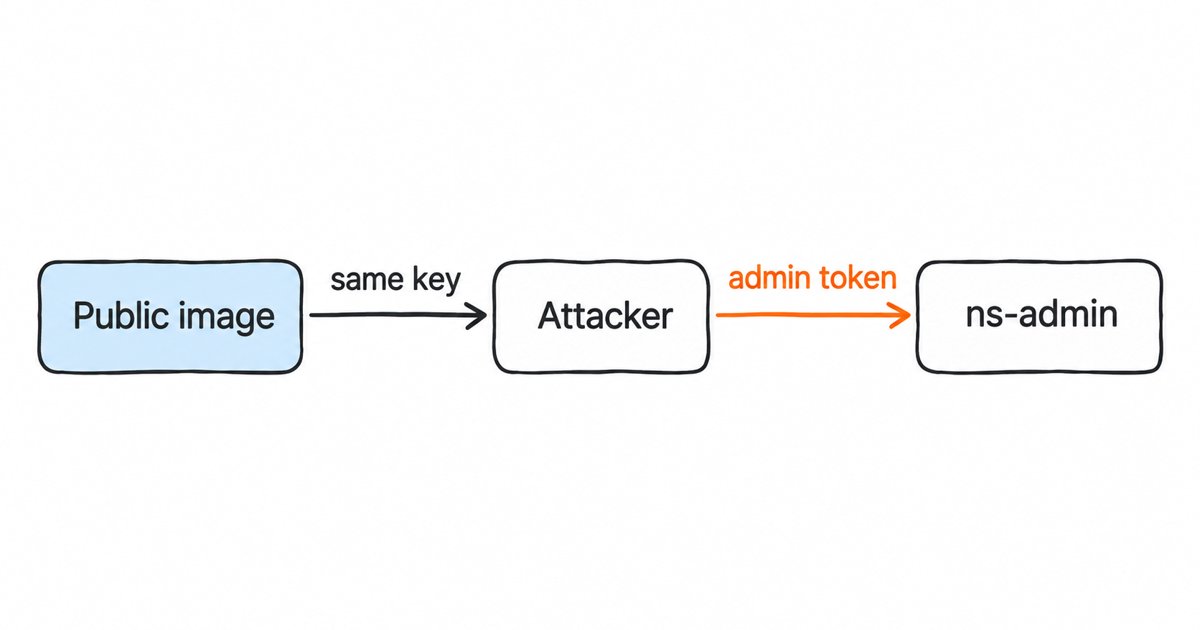
NextScan CVE-2026-126797: Hardcoded JWT Admin Key
CVE-2026-126797 lets anyone forge NextScan ns-admin admin tokens with a hardcoded HS256 key. Affected versions, exposure checks, mitigations and JWT…
13 min read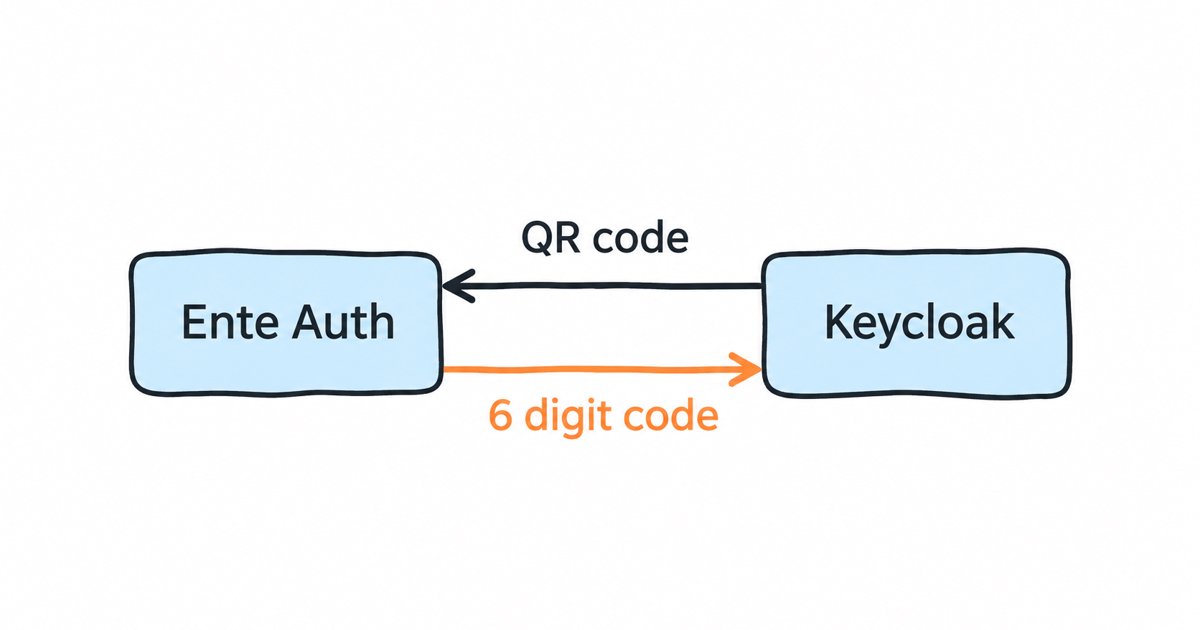
What Is Ente Auth and How It Works With Keycloak OTP
Ente Auth is a free, open source TOTP authenticator with end-to-end encrypted sync. Learn how its codes work and how…
11 min read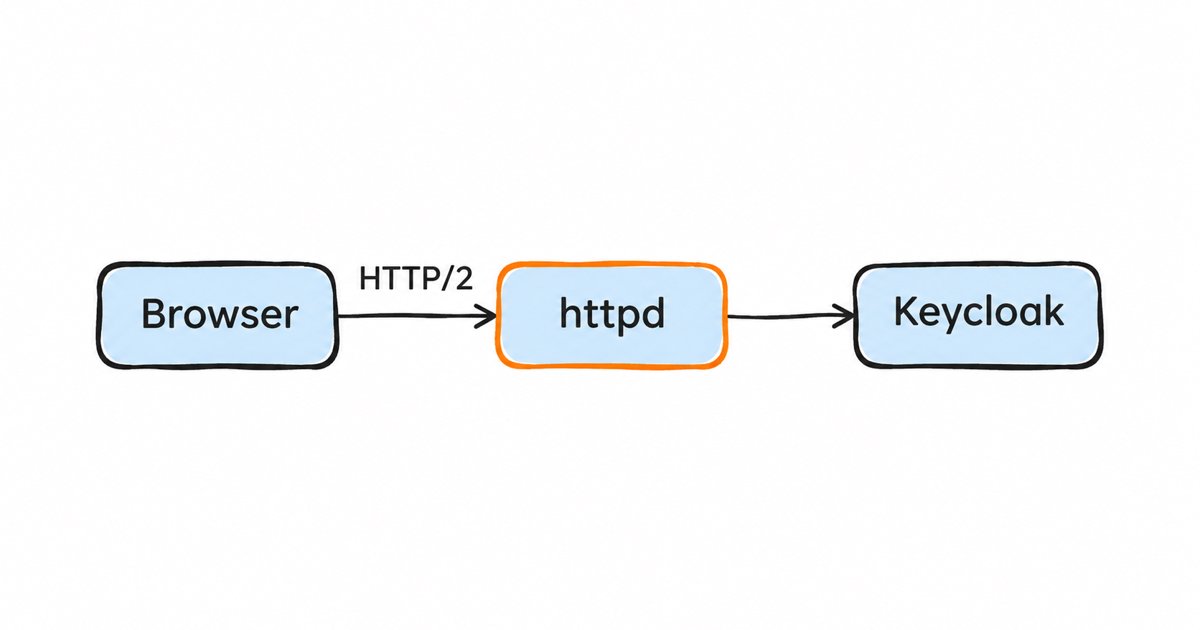
Apache mod_http2 CVE-2026-119618: Patch and Rotate Secrets
CVE-2026-119618 is a critical pre-auth RCE in Apache httpd mod_http2, 2.4.55 to 2.4.70. Patch to 2.4.71 or drop h2, then…
16 min read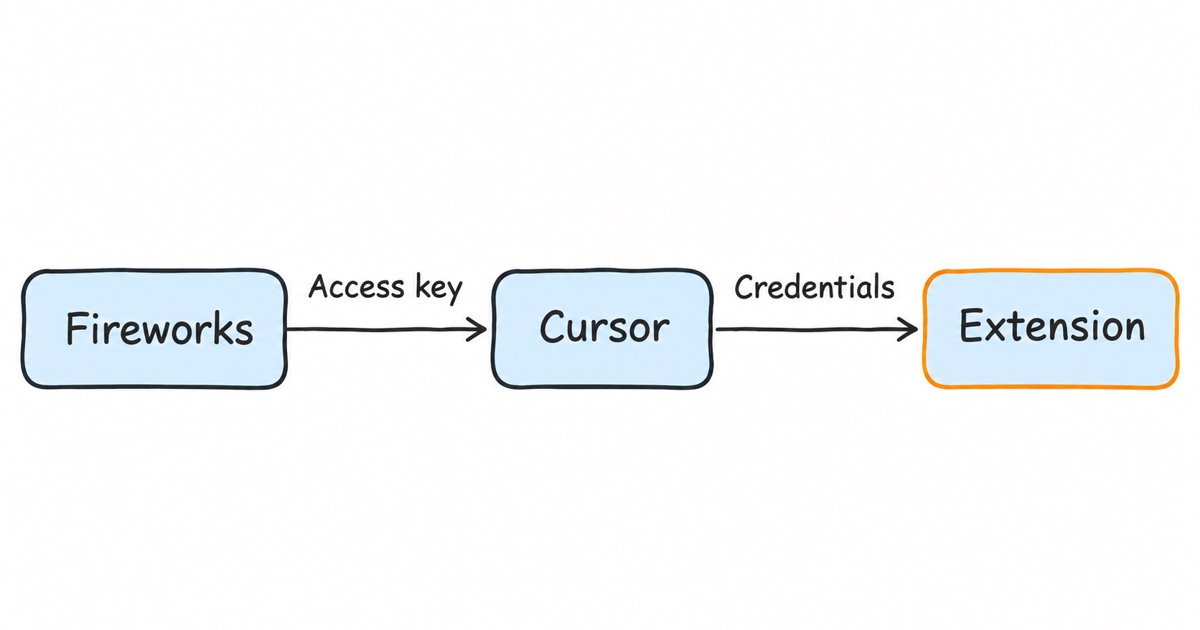
Cursor Supply Chain Attack: How a Fireworks AI Key Spread
A Cursor access key held by Fireworks AI led to tampered Claude Code extensions. What SecurityWeek reported, who must act,…
12 min read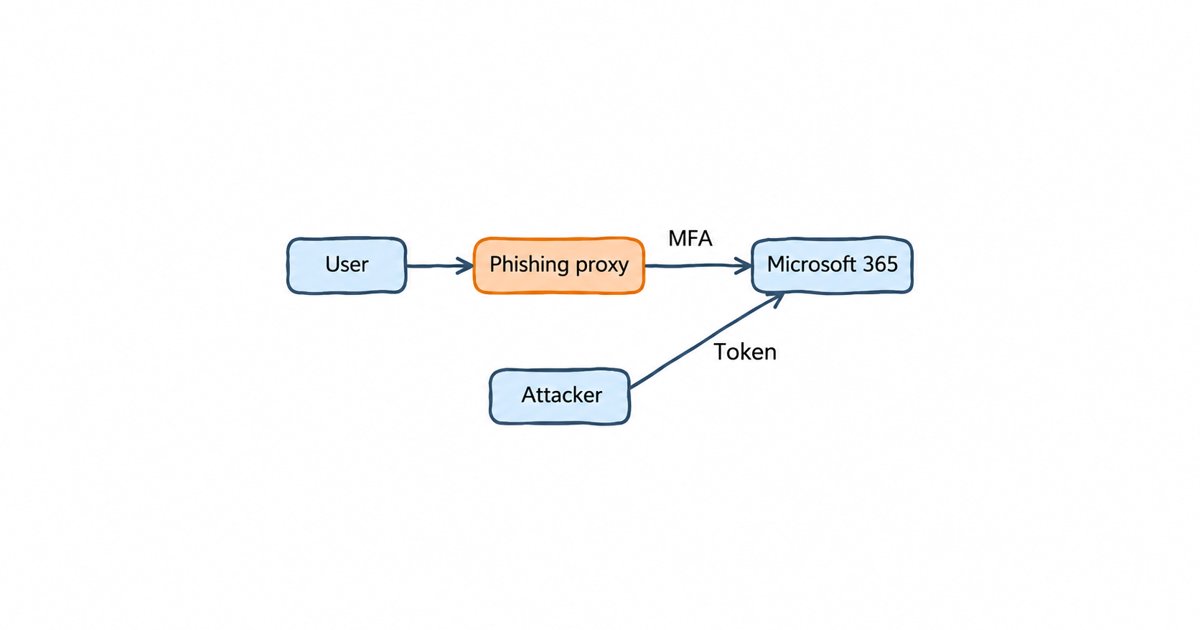
How Phishing Kits Replay Microsoft 365 Tokens, and the Fix
Phishing kits steal Microsoft 365 session tokens after MFA and replay them. How the replay works, and the Entra and…
12 min readStay ahead on identity & security
Get tutorials, product updates, and Keycloak tips delivered to your inbox.